Security Flaws in Popular Smart Toys
A popular interactive desktop robot toy called Eiliko transmits user voice data to overseas servers. Security researchers discovered that the companion AI stores transcripts and personal data without robust security measures, leaving the infrastructure open to potential unauthorized access.
Severe Data Exposure and Profiling
Manufacturer Energize Lab faces scrutiny following findings that the toy's associated cloud services lack basic protections.
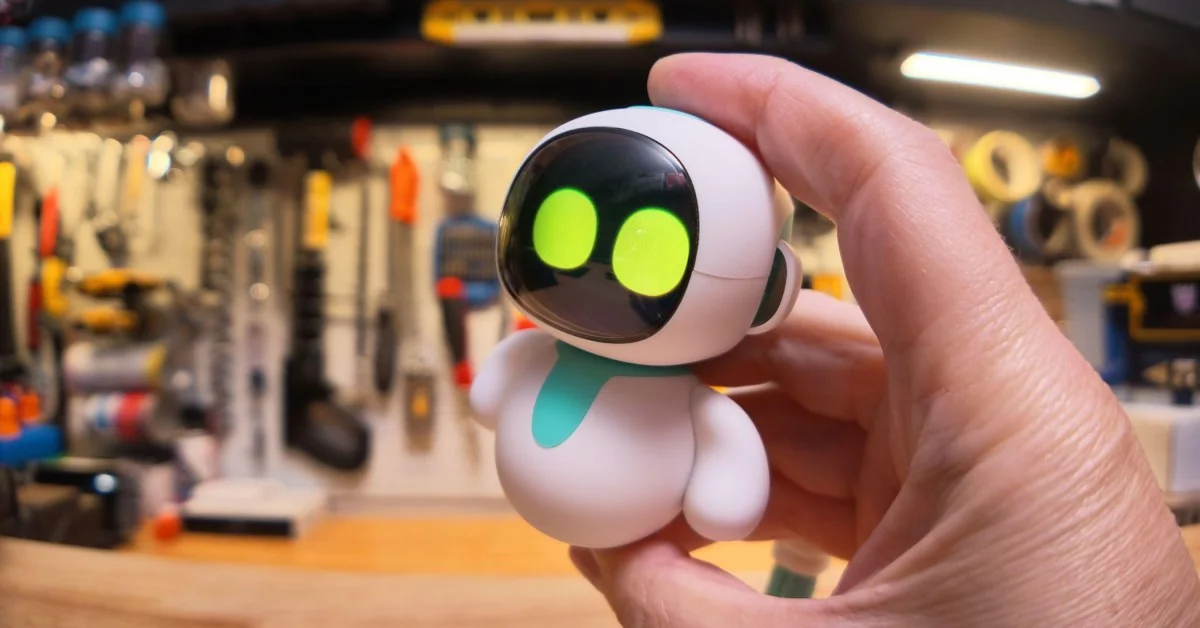
Eiliko.
An independent security audit involving an Eiliko unit revealed that routine voice interactions were logged extensively.
"Your secrets are safe with me," the device initially replied during testing.
In practice, investigators found that transcripts of user interactions could be accessed remotely within minutes of recording.
The exposed database reportedly contained millions of conversational records spanning tens of thousands of active devices globally, with a significant user base located in the United States, including children.
Security researcher Sammy Azdoufal, known for identifying vulnerabilities in various connected consumer hardware and smart home devices, uncovered the issues.
Azdoufal purchased the device during a retail trip and began analyzing its network traffic and companion application.
Lack of Encryption and Data Collection
Initial testing indicated that the manufacturer's backend service lacked authentication controls and actively compiled detailed behavioral profiles on users.
Azdoufal poses with the Eiliko he bought.
Beyond basic telemetry such as IP addresses, the system analyzed conversations to compile user profiles containing names, ages, personal relationships, and stated emotional states.
The compiled data included granular personal details that could potentially be leveraged by malicious actors for targeted social engineering or scams.
This sensitive information was stored alongside searchable full-text logs of user interactions and account credentials.
The investigation also found unencrypted audio snippets and media files stored at public web addresses accessible without authorization.
Short voice recordings and background audio captured by connected devices were similarly retrievable via unsecure endpoints.
These findings contradict the company's published privacy policy, which states that audio data is encrypted during transmission to cloud partners and deleted immediately after processing.
Response from Manufacturer and Remote Hijacking
Eiliko charges over USB-C, of course.
Attempts by investigators and journalists to contact Energize Lab regarding the vulnerabilities yielded little response, with support channels providing automated replies and staff declining to address the security disclosures.
Overseas sales representatives acknowledged receipt of messages but did not engage with the technical findings.
Subsequent follow-ups went unanswered by the company's management and technical teams.
Demonstrating the severity of the flaw, researchers were subsequently able to remotely modify the toy's memory and behavior profiles over the network.
Remote manipulation allowed unauthorized alteration of the device's responses, showcasing how weak backend security could be exploited to change an AI toy's generated dialogue.
During testing of the compromised toy, the device provided altered factual claims when queried by users.
The injected parameters overrode standard conversational parameters.
While certain baseline safety guardrails remained active for specific physical safety questions, other behavioral traits were successfully modified.
Inquiries regarding controversial topics returned unverified or uncertain responses.
Eiliko the dominatrix.
Subsequent testing proved that malicious updates could be pushed to alter the persona of connected devices across the active fleet.
The demonstration highlighted risks associated with insecure IoT devices connected to cloud-based large language models.
Researchers emphasized that similar vulnerabilities could theoretically affect mass deployments of smart hardware lacking proper transport layer security and authentication.
Consumer safety advocates recommend disabling network connectivity for vulnerable smart devices when manufacturers fail to address critical infrastructure security flaws.