Response to Security Flaws
Eiliko, a portable AI companion robot charm, faced intense scrutiny after researchers discovered significant security vulnerabilities allowing unauthorized access to user conversation transcripts.
Energize Lab Promises Security Overhaul
The maker of the device has acknowledged the severe flaws and stated that it plans to earn back consumer trust through verifiable security actions.
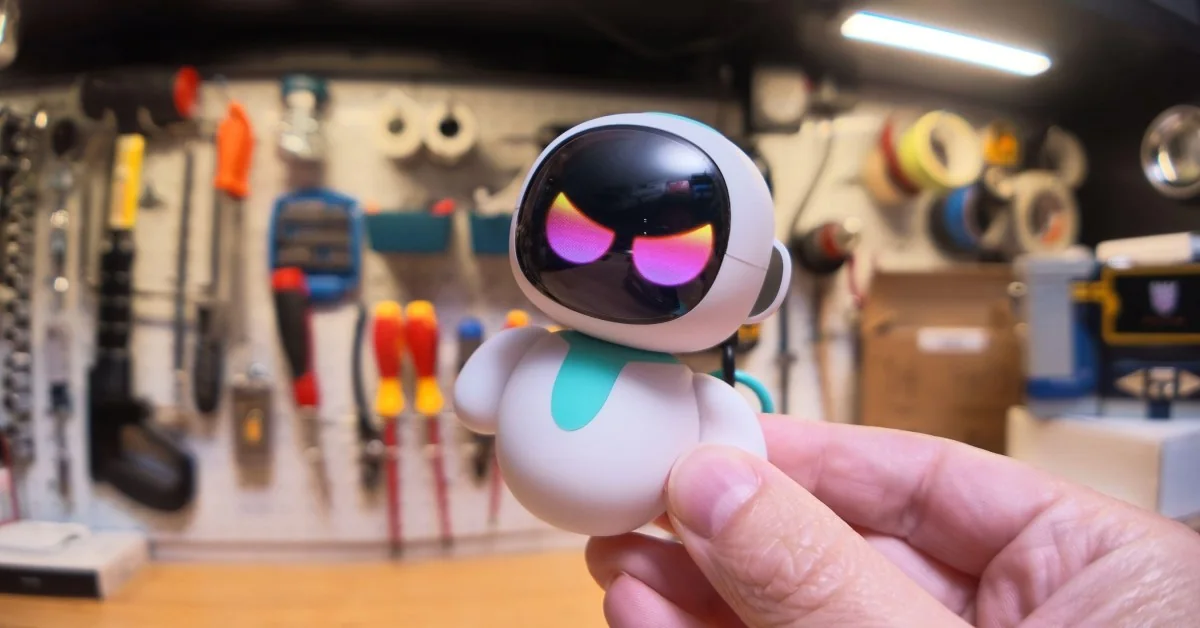
The Eiliko robot toy.
Energize Lab broke its silence regarding the reported security gaps following prolonged outreach by researchers and journalists.
In an official statement, the company confirmed it is addressing core issues identified in recent reports, hiring an independent security firm for a full systems review, and establishing a dedicated security contact email.
System Changes and Data Handling
Energize Lab stated that it closed external access to backend systems and disabled interfaces permitting remote modification of robot responses.
The manufacturer also pledged to cease storing conversation records and user profiles, committing to delete existing stored data including avatar images.
Long-term memory and custom avatar features will remain offline until security reviews confirm their safety, though the company intends to reintroduce personal data storage in the future.
Despite these promises, technical analysis indicated that some user audio recordings and photos remained accessible at unsecured public web addresses following the announcement.
Security researchers noted that remote administrative access mechanisms remained active on the devices, indicating that complete external lockdown had not yet been fully achieved.
Energize Lab reiterated its commitment to transparency, noting that institutional trust must be earned through sustained technical fixes over the coming weeks.
Here is Energize Lab’s full unsigned statement to The Verge:
Dear Sean, We sincerely apologize to you and to Mr. Azdoufal for not responding over the past month. This was our failure: After receiving the relevant information, we failed to sync with the technical team in a timely manner, and the subsequent troubleshooting also took some time. We have now set up a dedicated security inbox, security@energizelab.com, which is staffed and monitored. We thank you and Mr. Azdoufal for bringing these issues to our attention. We have confirmed the core issues identified in your reporting and are addressing each of them. As of today, we have: Closed all external access to our backend systems and rotated all access credentials; Disabled the interface that allowed a robot’s responses to be modified remotely; Taken the long-term memory feature offline. We no longer store conversation records or the user profiles generated from them; Taken the custom avatar feature offline. The app now offers built-in avatars only. We will delete stored conversation records, user profiles, avatar images, and related content. We are engaging an independent security firm to conduct a full review of our systems. The long-term memory and custom avatar features will not return until that review confirms they are secure. We will share an update on our progress once the review is completed. We started Energize Lab because we wanted to build small robots that bring a little joy into people’s lives. That idea only works if people can trust what is inside them, and we let them down. We know that words alone will not earn that trust back. We intend to earn it through what we do in the coming weeks, and we will keep you informed as we go. Sincerely, Energize Lab Team