Cyberattack Targets Medical Infrastructure
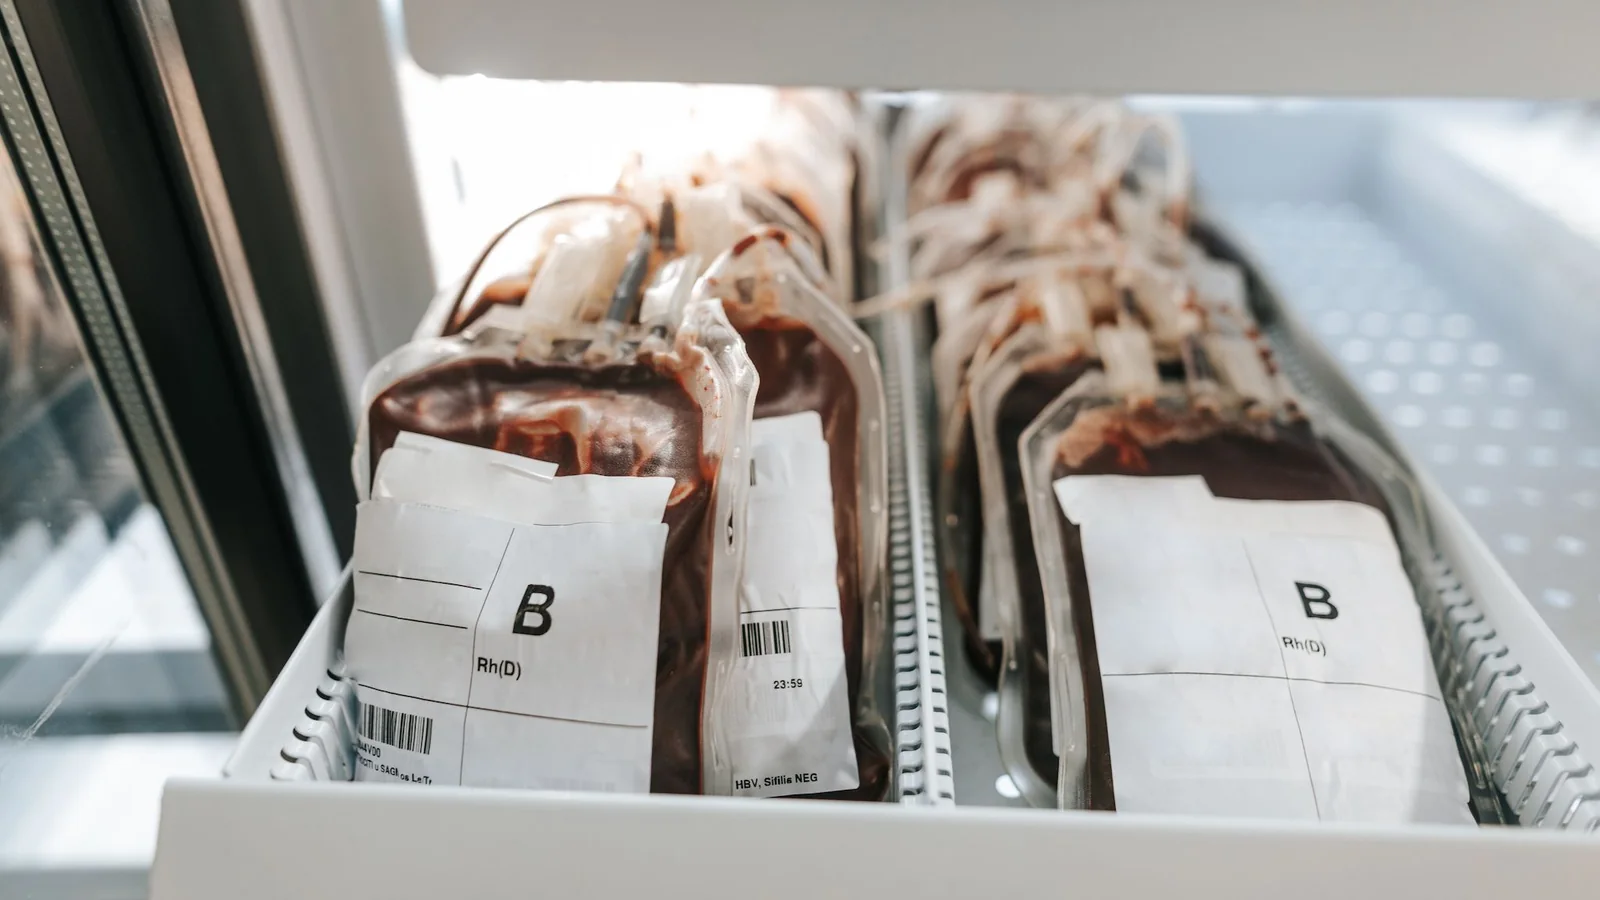
A fresh wave of cyberattacks has hit refrigeration units used by France's blood service (EFS). Thankfully, no biomaterials were lost, as the attack triggered the EFS' alerts, prompting staff to move the affected goods to proper storage.
The French Health Ministry said that the situation is being closely monitored and that no assets were lost. The attack seemed focused on refrigeration units at three sites, with Burgundy-Franche-Comté reportedly among them. The EFS' communiqué says the intrusion was on a service provider, which some outlets are reporting as Coolworld.
Coolworld has posted a notice stating that the incident was due to "remote monitoring software" used in its systems, pinning the cause on "a component from a third-party supplier." There are no technical details available yet, so it's not yet clear if the hackers found internet-reachable equipment, as they did with the supermarket attacks.
It's possible that Coolworld keeps the controllers inside its own network and that malfeasants had to first gain entry to said network. However, it's worth noting that it was the EFS' monitoring and alarm system that noticed something was up — not the vendor's.
Vulnerabilities in Industrial Controllers
The ongoing attacks seem to be happening on a per-vendor basis. Danfoss is the most-mentioned name — particularly, but not only, in the recent Nov. 1 - 2 attacks. Copeland/Dixell controllers were named in the Oct. 13 - 14 attacks.
A Danfoss datasheet recommends that its controllers are installed with "appropriately configured firewalls and secure LAN," and not "on any public or non secure network." The firm did issue a recent support bulletin clearly stating that the units should be installed with a VPN, but that document only appeared in October 2026.
The manuals for the Copeland/Dixell controller units that were hit in earlier attacks advise installers to map ports 80 (web) and 22 (Secure Shell) to the internet so that the units can be reachable from the outside, suggesting a VPN only as an option. The firm has since published a security advisory recommending that the units only be reachable from inside a VPN. This was published Oct. 14, after the first wave of attacks.
Attribution and Security Practices
Many news outlets claim to have seen materials in which Russia-aligned hacking groups Noname057(16) and Z-Pentest are claiming responsibility for the attacks. The purported hackers claim the attacks are about highlighting bad cybersecurity practices.
It's tempting to once again bring up AI agents as vehicles of cyber-destruction, but the reality is that, just like what happened with PHP, most of the time all bots are actually doing is revealing shoddy security practices and/or copious amounts of technological debt.